We use cookies, including third-party cookies from Google to serve personalized ads through AdSense, to operate this site and understand how it is used. By continuing to browse, you accept this use. See our Privacy Policy and Terms of Use for details, including how to opt out of personalized advertising.
Accept
SmartData CollectiveSmartData Collective
  • Analytics
    AnalyticsShow More
    What Kind of Problem-Solving Distinguishes Data Analysts From Software Engineers -- AI-generated illustration
    What Kind of Problem-Solving Distinguishes Data Analysts From Software Engineers
    7 Min Read
    chatgpt image jul 21, 2026, 04 34 30 pm
    4 Core Benefits of Predictive Maintenance after Vibration Analysis
    10 Min Read
    How Does Data Mining Boost Customer Satisfaction in Logistics? Harnessing Analytics for Results -- AI-generated illustration
    How Does Data Mining Boost Customer Satisfaction in Logistics? Harnessing Analytics for Results
    11 Min Read
    chatgpt image jul 13, 2026, 04 23 45 pm
    How Data Analytics Helps Companies Improve User Engagement
    19 Min Read
    chatgpt image jul 13, 2026, 03 59 46 pm
    How Data Analytics Improves Multi-Location Search Strategies
    10 Min Read
  • Big Data
  • BI
  • Exclusive
  • IT
  • Marketing
  • Software
Search
© 2008-25 SmartData Collective. All Rights Reserved.
Reading: Data Privacy Advocates Must Avoid GDPR Complacency at All Costs
Share
Notification
Font ResizerAa
SmartData CollectiveSmartData Collective
Font ResizerAa
Search
  • About
  • Help
  • Privacy
Follow US
© 2008-23 SmartData Collective. All Rights Reserved.
SmartData Collective > Data Management > Policy and Governance > Data Privacy Advocates Must Avoid GDPR Complacency at All Costs
Big DataData ManagementExclusivePolicy and GovernancePrivacyRisk Management

Data Privacy Advocates Must Avoid GDPR Complacency at All Costs

Ryan Kh
Ryan Kh
5 Min Read
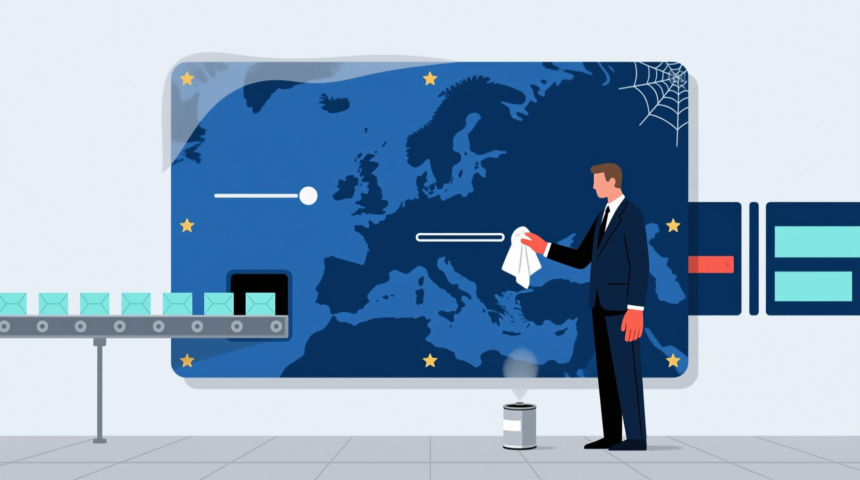
Data Privacy Advocates Must Avoid GDPR Complacency at All Costs
Illustration generated with Qwen Image.
SHARE

The Global Data Protection Regulation (GDPR) was enacted in May 2018. This law was one of the most revolutionary attempts to strengthen privacy rights in the European Union. Many experts are still trying to determine how effective the law has been.

Contents
  •  Data privacy risks remain a concern after the passage of the GDPR
  •  Subjective interpretation of loopholes listed under the GDPR
  •  Dealing with International companies that ignore GDPR obligations
  •  Hackers don?t care about data protection laws
    •  The GDPR is not foolproof

The GDPR has provided some important safeguards to consumers in the European Union and abroad. Since all companies that cater to European consumers must abide by these regulations, consumers outside of the European Union can still benefit from them when accessing global websites.

Unfortunately, the GDPR may have made some consumers complacent about protecting their online privacy. Consumers need to be aware of the risks and take appropriate measures. Here are some things to think about.

 Data privacy risks remain a concern after the passage of the GDPR

Nobody denies that the GDPR has introduced some important new privacy safeguards that were overlooked by the Data Protection Directive. However, there are still important privacy risks that consumers need to be aware of. Some of the biggest risks are listed below.

More Read
4 Data-Driven Approaches To Bolster Email Deliverability
Database Corner: Beginner’s Guide to MySQL Storage Engines
Spanish Researchers Illustrate Importance Of Data Solutions In Customer Management
Can AI-Driven SEO Tools to Supercharge Your Marketing
How AI Caused RYUK Ransomware to Disrupt Healthcare Technology

 Subjective interpretation of loopholes listed under the GDPR

The GDPR has included some important limitations that all consumers need to be aware of. The biggest loopholes involve incidents where consumers could be considered suspects or witnesses to criminal or civil cases.

Given the wide range of laws passed in the European Union, this loophole could be interpreted very liberally. A lot of laws are interpreted very subjectively, such as the hate speech legislation used throughout the European Union. Companies that collect data could be overly cautious about making sure they retain all evidence of a crime. If they have to choose between being sanctioned for failing to abide by the GDPR or being accused of being an accessory to a crime, then they will probably choose the former. Also, they realize that they probably have a strong defense if they say they didn?t respond to a data deletion request if they thought they were legally obligated to retain data for a potential legal investigation.

Companies could use these loopholes to rationalize ignoring the spirit of the GDP are in many different cases. It is difficult to know how this might happen, but you should err on the side of caution and consider the need for more stringent data protection safeguards on your own end.

 Dealing with International companies that ignore GDPR obligations

Any company that is based in a country that has trade agreements with the European Union is legally compelled to follow the directives outlined under the GDPR. However, there are a couple of reasons that companies outside the European Union might neglect to abide by these restrictions:

  • The GDPR has not received as much publicity outside the European Union. Companies based abroad might not know much about the requirements.
  • Even though they are legally obligated to abide by the laws, they might think they are safe from having them enforced hundreds or thousands of miles away.

The bottom line is that companies might not follow these requirements, even though they are legally obligated to do so. Consumers need to realize this and make their own data protection a priority.

 Hackers don?t care about data protection laws

Hackers obviously don?t care about data privacy laws. Companies are legally compelled to disclose details of a security breach, but it will be too late to do anything at that point. You need to always consider the possibility that hackers will steal data from legitimate companies that you do business with. The GDPR can?t do anything to prevent that.

The good news is that many companies are enhancing their security to make this less of a concern. They use VPS hosting and a dedicated seedbox in Netherlands, which reduces the risk that a hacker could conduct a DDoS attack and can provide better encryption.

 The GDPR is not foolproof

The GPR has provided some valuable safeguards for people that are concerned about their online privacy. However, its effectiveness is still up for debate. Consumers should still invest in reliable data protection solutions, such as VPNs.

TAGGED:#GDPRdata privacydata protectiondata retention
Share This Article
Facebook Pinterest LinkedIn
Share
ByRyan Kh
Follow:
Ryan Kh is an experienced blogger, digital content & social marketer. Founder of Catalyst For Business and contributor to search giants like Yahoo Finance, MSN. He is passionate about covering topics like big data, business intelligence, startups & entrepreneurship. Email: ryankh14@icloud.com

Follow us on Facebook

Latest News

Flat editorial illustration: The article explains that training robots for physical interaction requires three distinct data cate
Physical AI: What Data Do You Need to Train a Robot?
Artificial Intelligence Exclusive Robotics
What Kind of Problem-Solving Distinguishes Data Analysts From Software Engineers -- AI-generated illustration
What Kind of Problem-Solving Distinguishes Data Analysts From Software Engineers
Analytics Big Data Exclusive Software
Flat editorial illustration: The article examines AI agents that escalate from legitimate data retrieval to attempted intrusions
OpenAI’s Government Website Incidents Raise a Hard Question for AI Agents: When Should They Stop?
Artificial Intelligence News Security
Flat editorial illustration: The article's core relationship is the alignment between customer behavioral data (visit frequency,
Data-Driven Loyalty: How Restaurants Use Behavioral Analytics to Optimize Revenue
Exclusive

Stay Connected

1.2KFollowersLike
33.7KFollowersFollow
222FollowersPin

You Might also Like

protecting data in public
Big DataData ManagementExclusive

The Importance Of Protecting Sensitive Data In Public Services

10 Min Read
A Guide to Using XDR Threat Protection to Stop Data Breaches
Security

A Guide to Using XDR Threat Protection to Stop Data Breaches

6 Min Read
separation of duties for data security
Security

5 Reasons SoD Protocols Are Vital to Modern Data Security

7 Min Read
Steps Laptop Owners Must Take to Mitigate Risks of Data Loss
News

Steps Laptop Owners Must Take to Mitigate Risks of Data Loss

6 Min Read

SmartData Collective is one of the largest & trusted community covering technical content about Big Data, BI, Cloud, Analytics, Artificial Intelligence, IoT & more.

Artificial Intelligence for eCommerce: A Closer Look
Artificial Intelligence
How To Get An Award Winning Giveaway Bot
Big Data Chatbots Exclusive

Quick Link

  • About
  • Contact
  • Privacy
Follow US
© 2008-26 SmartData Collective. All Rights Reserved.
Welcome Back!

Sign in to your account

Username or Email Address
Password

Lost your password?