We use cookies, including third-party cookies from Google to serve personalized ads through AdSense, to operate this site and understand how it is used. By continuing to browse, you accept this use. See our Privacy Policy and Terms of Use for details, including how to opt out of personalized advertising.
Accept
SmartData CollectiveSmartData Collective
  • Analytics
    AnalyticsShow More
    What Kind of Problem-Solving Distinguishes Data Analysts From Software Engineers -- AI-generated illustration
    What Kind of Problem-Solving Distinguishes Data Analysts From Software Engineers
    7 Min Read
    chatgpt image jul 21, 2026, 04 34 30 pm
    4 Core Benefits of Predictive Maintenance after Vibration Analysis
    10 Min Read
    How Does Data Mining Boost Customer Satisfaction in Logistics? Harnessing Analytics for Results -- AI-generated illustration
    How Does Data Mining Boost Customer Satisfaction in Logistics? Harnessing Analytics for Results
    11 Min Read
    chatgpt image jul 13, 2026, 04 23 45 pm
    How Data Analytics Helps Companies Improve User Engagement
    19 Min Read
    chatgpt image jul 13, 2026, 03 59 46 pm
    How Data Analytics Improves Multi-Location Search Strategies
    10 Min Read
  • Big Data
  • BI
  • Exclusive
  • IT
  • Marketing
  • Software
Search
© 2008-25 SmartData Collective. All Rights Reserved.
Reading: Only 18% of Software Apps Pass Security Tests
Share
Notification
Font ResizerAa
SmartData CollectiveSmartData Collective
Font ResizerAa
Search
  • About
  • Help
  • Privacy
Follow US
© 2008-23 SmartData Collective. All Rights Reserved.
SmartData Collective > IT > Security > Only 18% of Software Apps Pass Security Tests
SecuritySQL

Only 18% of Software Apps Pass Security Tests

AlexOlesker
AlexOlesker
0 Min Read
Only 18% of Software Apps Pass Security Tests
Photo by padrinan on Pixabay (https://pixabay.com/photos/memory-magnetic-floppy-disk-old-2882481/)
SHARE

Over the past 18 months, almost 10,000 software applications from the government and private sector were submitted to Veracode’s online security testing platform for independent security auditing and 8 out of 10 failed to achieve an acceptable level of security on their first try. Veracode reached this conclusion by automatically checking submitted apps for over 100 types of flaws. That’s not to say the 18% that passed were flawless, merely that their security gaps weren’t glaring. Take into account that developers who have their applications tested by an independent third party are likely more security conscious to begin with, and you paint a pretty grim picture or software application security.

In government, 75% of applications had cross-site scripting problems, which means that attackers could find ways to input malicious code onto a webpage. These attacks are often used to get sensitive information maintained by a user’s browser, such as session cookies that can then be utilized to impersonate the  user. According to Veracode, one reason for the prevalence of cross-site scripting issues was that many government apps were built using Cold Fusion, a programming language more likely to produce such flaws than languages more commonly used for commercial applications. In addition, 40% of government applications were vulnerable to SQL injections, which allow unauthorized users to get into back-end databases through a website. SQL injection flaws have grown less common over the past few years in the app market as a whole, but they have failed to improve in government despite all of the “wake up calls” declared earlier when LulzSec used this method of attack along with cross-site scripting to hack government and industry websites. Veracode CTO Chris Wysopal believes that while companies have to deal with angry customers, the government only needs to worry about meeting regulations and standards and hence faces less pressure to develop secure applications.

That doesn’t mean that commercial software apps fared much better, they simply had a more diverse set of problems such as buffer overflows and management issues. Veracode found that 3% of commercial applications had backdoors, initially put in place for debugging and diagnostic support, that can be used by attackers. They also looked at about 100 Android enterprise mobile applications and found that 40% had hard-coded crypographic keys, which are keys that are fixed in the source code. If the mobile device is lost or stolen a thief could get into the application without additional credentials or a hacker could decomplie the source code to get the key.

This startling data confirms that government and industry alike should assume that their applications are vulnerable. Rather than responding to incidents reactively, they should presume breach and make sure their auditing and remediation processes are in order. They should also try to pinpoint what their vulnerabilities are, as in all likelihood their applications are flawed,  with the help of services such as Veracode. This way, they can prevent breaches or at least make vulnerabilities harder to find.
More Read

AI Drives the Intersection of Industrial Hygiene and Cybersecurity
Managing Big Data? Make Sure You Know the Challenges
Why Publish Your Data?
The Information Governance Practices That High-Demand Social Work Roles Require
Could Cryptocurrency Be the Answer to Accounting Fraud?
Share This Article
Facebook Pinterest LinkedIn
Share

Follow us on Facebook

Latest News

Flat editorial illustration: The article's core relationship is workload-by-workload decision-making for cloud migration, where s
Which Workloads Should Move to the Cloud?
Cloud Computing Exclusive IT
Flat editorial illustration: The article positions data governance as a strategic board-level concern rather than a purely techni
Why Data Governance Is Becoming a Board-Level Business Priority
Big Data Exclusive Policy and Governance
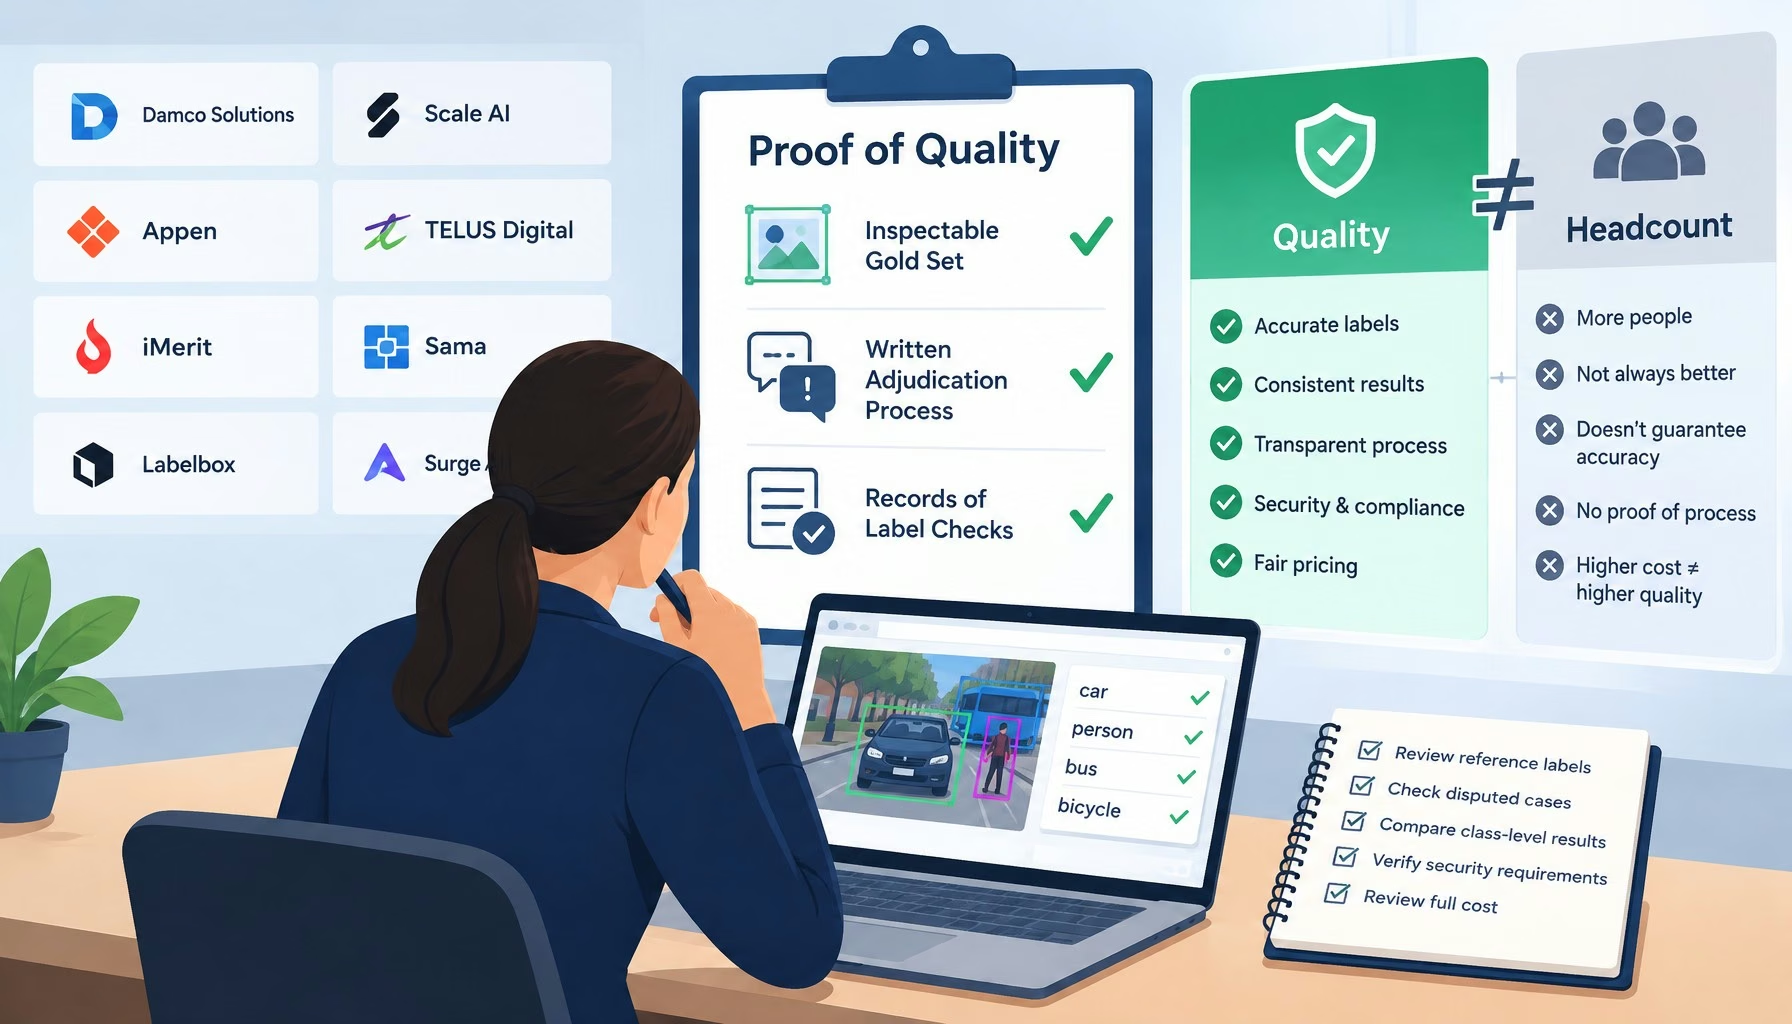
Flat editorial illustration: The article argues that data annotation quality should be measured by inspectable gold sets, written
The Top Data Annotation Companies Are Separated by Proof of Quality, Not Headcount
Big Data Exclusive
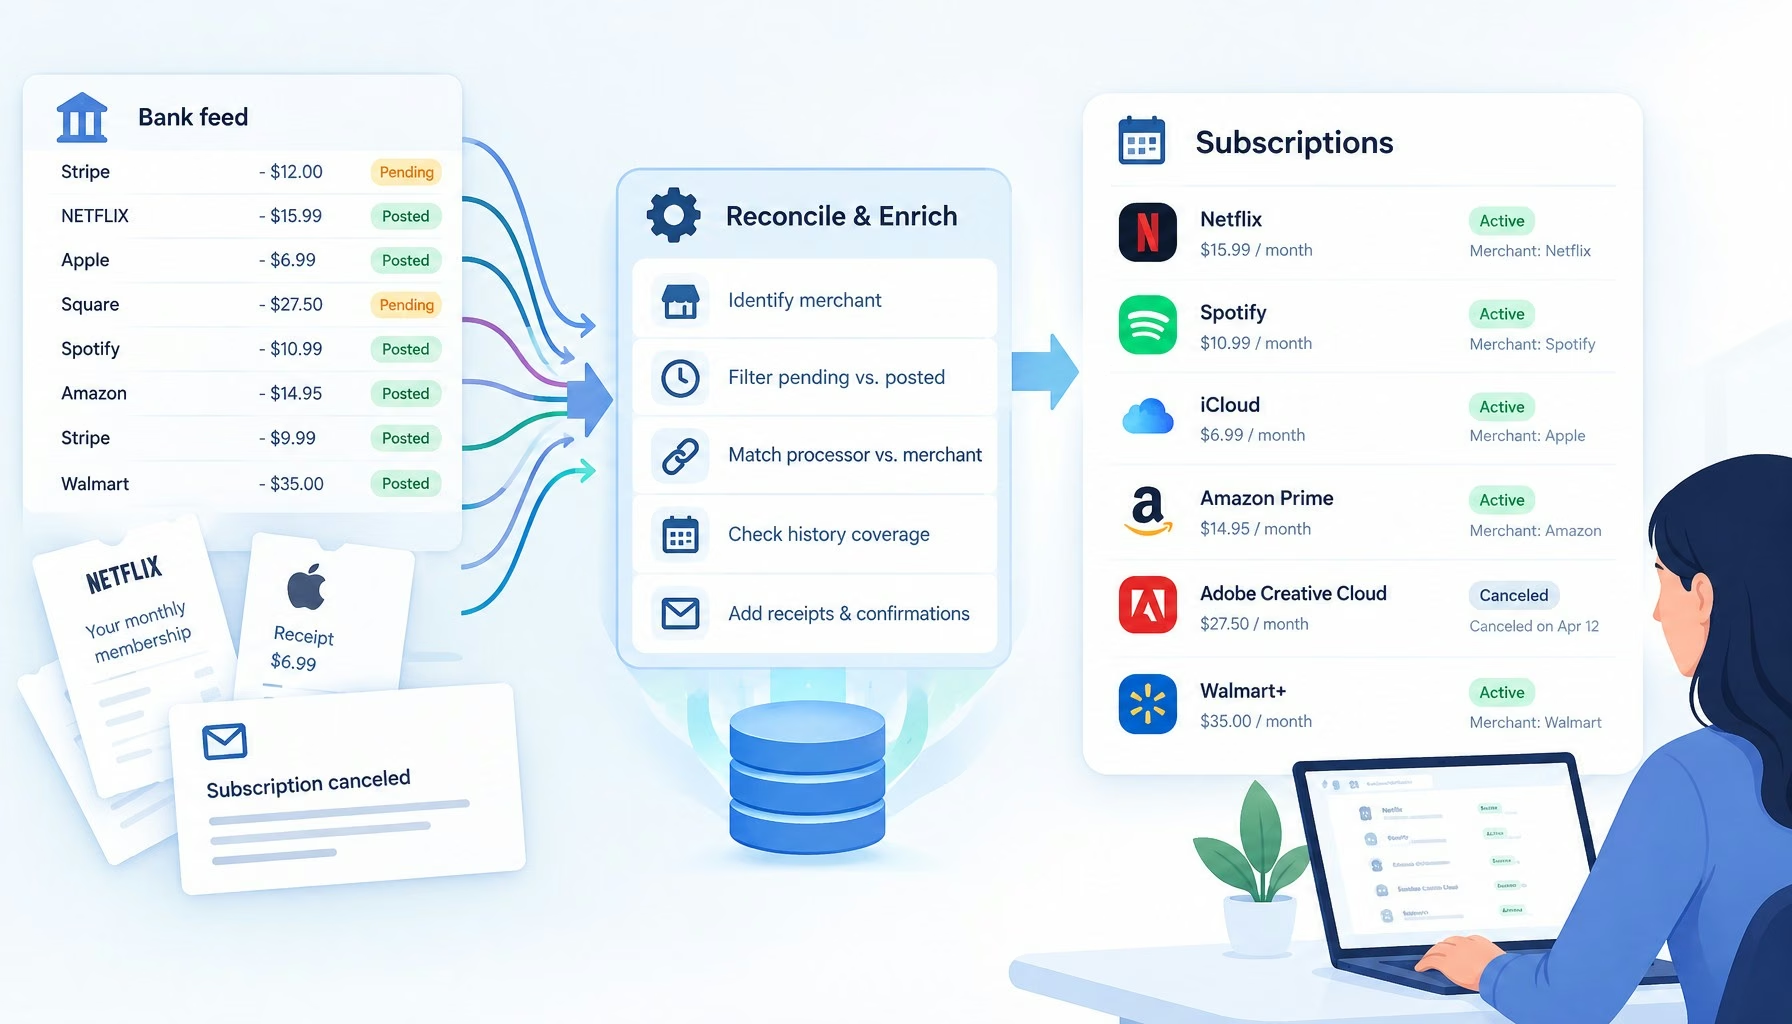
Flat editorial illustration: The article's core relationship is the gap between raw bank-feed records and reliable subscription i
Subscription Trackers Have a Transaction Data Problem
Big Data Exclusive

Stay Connected

1.2KFollowersLike
33.7KFollowersFollow
222FollowersPin

You Might also Like

The Secret cPanel Hack For A Secure Big Data Website
Data Management

The Secret cPanel Hack For A Secure Big Data Website

11 Min Read
Should the Entire Internet Be Encrypted?
Data MiningLocationSecurity

Should the Entire Internet Be Encrypted?

6 Min Read
Database Corner: Beginner’s Guide to MySQL Storage Engines
AnalyticsBig DataSQL

Database Corner: Beginner’s Guide to MySQL Storage Engines

8 Min Read
Tips to keep your eCommerce Store Secured against Hackers
ITPrivacySecurity

Tips to keep your eCommerce Store Secured against Hackers

4 Min Read

SmartData Collective is one of the largest & trusted community covering technical content about Big Data, BI, Cloud, Analytics, Artificial Intelligence, IoT & more.

AI chatbots
AI Chatbots Can Help Retailers Convert Live Broadcast Viewers into Sales!
Chatbots
How To Get An Award Winning Giveaway Bot
Big Data Chatbots Exclusive

Quick Link

  • About
  • Contact
  • Privacy
Follow US
© 2008-26 SmartData Collective. All Rights Reserved.
Welcome Back!

Sign in to your account

Username or Email Address
Password

Lost your password?