Trend Micro’s one-time password (OTP)-based two-factor authentication bypass report (PDF) is hardly news to those in the tech world, but it is well-packaged and even branded with a weird name – Operation Emmental (also known as Swiss cheese) – how media-ready!
The story is the same: Good ol’ phishing email pretending to be from a real bank contains malware in an embedded attachment. When clicked, the file downloads and executes another file pretending to be a Windows update – instead, it installs malware!
That malware does a few things – changes DNS settings and redirects to the attacker’s servers; installs a new SSL certificate in the user’s system; and deletes itself without leaving a trace (rendering anti-malware software useless after the fact).
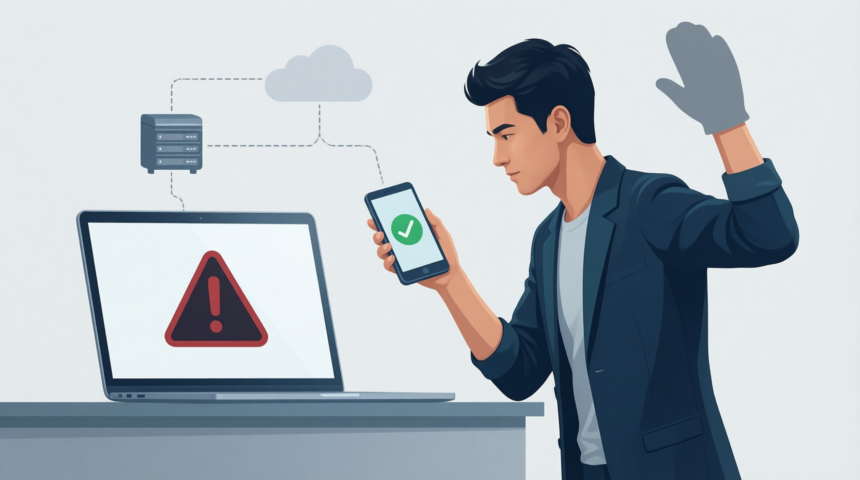
When users attempt to visit their bank’s landing page, they get redirected to a fake bank page that steals their username/password. Then, they’re asked to type in the one-time password (OTP) sent by their bank’s mobile app – but, the SMS never arrives, so then the website prompts the user to install a malicious mobile app that’s pretending to be an OTP generator. Whew.
This malicious Android app actually intercepts the real two-factor SMS tokens sent by the bank, thereby gaining access to the user’s account and stealing all their monies.
A History of OTP-Based Bypass Malware
Back in March, I wrote about the research of Dell SecureWorks that presented their work, Cryptocurrency-Stealing Malware Landscape at this year’s RSA Conference in San Francisco. While this was referring to online banking wallets for currencies like Bitcoin, it also holds true for traditional online banking. A quote from their report found the same thing, that malware can bypass OTP-based two-factor, albeit with a slightly different approach:
Many exchanges have implemented two-factor authentication using one-time PINs to combat unauthorized logins. However, more advanced malware can easily bypass OTP-based 2FA, by intercepting the OTP as it is used and creating a second hidden browser window in order to log the thief into the account from the user’s own computer.
As Duo Security’s Senior Security Researcher Zach Lanier states:
This is precisely why we emphasize push over SMS. The latter is too fallible, and this particular malware / campaign is just another in a long line…Zitmo (“Zeus in the Mobile”) being one of the original malware families to intercept one-time passwords that are delivered via SMS (and targeting banks in Europe).
Yup, it’s true – back in 2010, Trend Micro wrote another blog reporting that certain Zeus variants could break into bank accounts despite being protected by OTP two-factor authentication.
Media Perspective: Overgeneralizing Two-Factor Authentication
Yet the media coverage doesn’t go deep enough into variances of different two-factor solutions:
Most sites ask for a single password. But two-factor authentication systems require customers to enter a second, one-time password that has been emailed or texted to their phones. The hope is that a second identifying factor eliminates the risk that criminals can break into customers’ accounts simply by stealing an online password. – NYTimes.com, Hackers Find Way to Outwit Tough Security at Banking Sites
The problem is, many media articles resulting from the report are woefully simplistic, glossing over the fact that not all two-factor authentication solutions are created the same. Two-factor authentication does not translate to one-time passwords, exclusively.
All of this OTP-based 2FA bypass talk just makes more of a case for push notification-based two-factor authentication, the preferred and most secure method to protect against the most varied of attacks.
A Better Alternative to OTP: Out-of-Band Authentication (OOB)
An out-of-band authentication solution can protect against man-in-the-browser attacks and other attempts to steal a one-time password. Plus, it’s already recommended by the FFIEC for online banking security guidelines to protect transactions. Their take on it is:
Out-of-band authentication means that a transaction that is initiated via one delivery channel (e.g., Internet) must be re-authenticated or verified via an independent delivery channel (e.g., telephone) in order for the transaction to be completed. Out-of-band authentication is becoming more popular given that customer PCs are increasingly vulnerable to malware attacks.
Instead of using a one-time password or pin, some modern two-factor solutions allow you to authenticate via push notifications on your smartphone with the help of a secure mobile app. It’s important to check that your two-factor solution provides different methods to fit your organization’s needs, and isn’t limited to only SMS or token-based authentication.
Additionally, the design of the security solution matters – your users’ phones and your two-factor provider’s servers should be set up to validate each other to prevent network-level attacks against the authentication process.
A little more about Duo Security’s two-factor method using push notifications (Duo Push):
Duo Push leverages the capabilities of modern smartphones to create a more secure and user-friendly two-factor authentication experience. Specifically, Duo Push utilizes the native push notifications (APNS, C2DM, etc) to provide real-time notification of transaction and login requests to a user’s smartphone, a secure out-of-band (OOB) communications protocol to display the full verified details of the request to the user, and simple one-touch responses to allow the user to approve or deny the request on the smartphone itself.
While this blog relates more to protecting against RSA-style breaches by “ditching the traditional shared secret model of OTP-based two-factor,” it’s also a good explanation of Duo Security’s push cryptography: RSA-Proofing our Duo Push Two-Factor Authentication.
Ultimately, OTP-based two-factor authentication using SMS just isn’t the best solution, as shown in these bypass scenarios. And that’s exactly why Duo Security has designed a more secure out-of-band authentication solution to outpace remote attackers and protect against threats that many older, legacy two-factor authentication solutions cannot. Find out more about what your solution should include in our Two-Factor Authentication Evaluation Guide.