A new version of ransomware has been detected recently that not just holds the data hostage and the victim’s machine until a ransom has been paid but also has the machine exploited as a part of DDoS attack. This implies that the victim cannot access the endpoint. Service is denied to another victim utilizing the same end point. This results in two attacks.
The attacker utilizes a weaponized Office document for infecting a system. The reason why this method is being employed by most of the attackers is the “next-gen”, and other antivirus vendors are blind to such attacks.
For a file-less attack, Visual Basic is exploited by the attackers. Visual Basic is a popular and widely used programming language that is employed today. Automation tasks that are native to Windows are employed. This has turned into the go-to-scripting language as it is widely used on the platform offered by Windows. Embedding of VB scripts is done within text documents which permits the users to conduct legitimate business tasks and to generate reports as well. Black hats employ the same technique for crafting weaponized documents that can run malicious codes on the host system. Analysis of the attack has been included within this post.
An attacker sends a phishing email to a victim with the attachment in Rich Text Document (.rtf) format. In several instances, the message and the document pretend to reflect important information or invoice that could be time sensitive. The document seems to have a filename that is computer generated. When the victim still decides to open the attachment that consists of the weaponized document, the system gets infected when there is an initiation of the macros embedded.
More Read
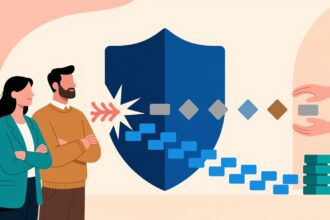
A document can only execute when it has gained the status of the administration in the host system. The user is prompted to run the macros which grant elevated privileges to the malicious document. An elevated command shell is spawned on the host. This executes the VB script that has been encoded.
Obfuscation is commonly employed by attackers to confuse the researches by manipulating the code. In such cases, the functions are all variables that seem to have been generated by the computer. Although human readable functions are also present in pieces of code, randomized font is still utilized for lower and upper case text. Regular conventions are not followed.
The code has to be reformatted by the experts with the use of line breaks that are proper. The variables that have been instantiated can be seen at the end of each line. These also consists of integers, comments, and variables for confusing the reader.
When a script is formatted with regular convention, it reveals that the code stands for something real. It carries information about the characteristics of the malware. An FOR loop is seen in the first snipper that iterates from one to half the length of the variable. Variables broken down into integers are present within the FOR loop. These variables break down to integers. The formatted function can be seen in the second snippet of the code.
In weaponized documents, an object is opened with a function that has been set on a particular variable. Data is written into another text file until the stream terminates. The stream is closed once done, and the variables that are remaining are reset. The entire script is exported to .vbs file at the end of the code.
Once a script is executed, a malicious binary ‘3311.tmp’ is created. This is then executed later. Binary seems to be a ransomware belonging to the Cerber family as per the analysis of the statistics done. Evidence of ransomware has been proven by dynamic analysis. The binary ransomware makes alternations in the screensaver data. These changes permit the attacker to post a ransom note on the screen of the victim.
This variant of ransomware exhibits a strange behavior in comparison to other ransomware. When a dynamic analysis was done on binary, it was noticed that the host called out to a subnet 255.255.192.0. The range of address begins from 85.93.0.0 and reaches up to 85.93.63.255. It is not possible to tell whether the binary ran to completion or not. The repetition of a sequence of events was also commonly noted in binary. The explorer .exe is launched after the creation of a hexadecimal tmp file.
All events are processes of the malicious file that was created originally. The “dnscacheugc.exe” file has the same hash but a different file name as the 3311.tmp file. The sequence of events has a connection with the original loop seen in the VB script. The purpose of the use of .tmp files is still unclear. This is because these barely have any role to play in the execution. This makes the security experts believe that the malware failed to execute completely and also the payload delivery.
Binary malware where documents are being weaponized serves a plethora of purposes. This typical ransomware encrypts the file system of the user. The files are encoded, and a ransom note is displayed on the screen. This binary has the potential to be used for a DDoS attack. The network traffic, when monitored, seems to be flooded. The UDP packets and the subnet are flooded over port 6892. When the source address is spoofed, the response traffic of the host gets directed to a targeted host from the subnet. This causes the host to become unresponsive.
Ransomware threats are growing in number, and new techniques are being employed so that the attacks cannot be defended by the host system or any form of security.